SPECIALISE
For ISO 27001, NIS2, DORA, EU AI Act or CSRD. Four variants of one core model: one evidence source, many tests.
Same methodology. Four typical triggers.
Frameworks overlap. Our methodology exploits that: collect evidence once, use it many times.
Compliance by Design
ISO 27001, SOC 2, NIS2, DORA. Audit on the horizon or ongoing governance pressure.
Cross-framework map: one evidence covers multiple tests. We embed controls directly into your workflow, not as a separate spreadsheet. You end up with a living control board, audit-ready evidence pack, and a clear gap and remediation backlog.
- Control map (process → requirement → evidence)
- Cross-framework mapping (ISO 27001 / NIS2 / DORA / SOC 2)
- Audit-readiness brief with scorecard
- Evidence pack (PDF binder + XLSX)
- Pre-audit workshop and fieldwork support
After audit: SUSTAIN retainer for annual re-certification and control upkeep.
Tool Readiness
ERP, CRM, HRIS, ITSM. Tool implementation pending or prerequisites require documented processes.
Data structures, roles, processes. Sorted before the rollout. We translate your target processes into functional and technical requirements for the vendor. Standard configuration where possible, customisation only where truly required.
- Functional requirements per process
- Vendor gap analysis
- Configuration recommendations
- Data model blueprint (YAML + ERD)
- Cutover and training plan
During and after the rollout: Fractional CIO as vendor counterpart and escalation lead.
AI Governance Readiness
EU AI Act, ISO 42001. AI in use or planned.
EU AI Act obligations live in your operating model, not in a separate AI pack. We map your AI systems: inventory, transparency, human oversight, vendor governance. All integrated across your existing controls. One evidence suite covers AI Act + GDPR Art. 22 + ISO 27001 + NIS2.
- AI register with risk classification (unacceptable / high-risk / limited / minimal)
- Transparency and human-oversight procedures
- Vendor due-diligence for AI systems
- Incident and reporting workflow
- Cross-framework mapping (AI Act / GDPR Art. 22 / ISO 27001 / NIS2)
Ongoing AI governance obligations: Fractional CIO / NIS2 Named Person / Fractional CISO. For the target-state operating model: EQUIP IT Ops & InfoSec and Product Engineering / SDLC.
CSRD & ESG Reporting Readiness
CSRD, ESRS, GRI. First reporting cycle approaching or assurance has flagged evidence gaps.
Double materiality, data flows, auditable reporting. We surface data sources, map them to ESRS data points, and build the process so those numbers are collected continuously, not frantically assembled at reporting time.
- Materiality matrix (double materiality)
- ESRS data-point mapping
- Data-flow and ownership diagram
- Continuous ESG data-capture process
- First report draft with gap analysis
SUSTAIN for annual reporting and process upkeep.
Tier 1 as baseline. Tier 2 in context.
Tier 1 frameworks apply to every organisation in our scope: the universal baseline every engagement and every EQUIP pack works from. Tier 2 frameworks apply when the client's context triggers them, native to the relevant pack or delivered as a delta-instruction overlay. Evidence collected once covers multiple tests.
German national frameworks (BSI IT-Grundschutz, BSI C5, TISAX, BAIT/VAIT/KAIT/ZAIT, GoBD, HinSchG, LkSG) are not part of our standing capability set. Available on request per engagement, but not productised.
6–14 weeks. Five phases.
Scope
Which frameworks, timeframe, business units.
Gap analysis
Where you stand today, per control. Collect evidence.
Remediation
Close gaps. Build artefacts. Harden processes.
Mock audit
External senior plays auditor. Findings fixed.
Handover
Evidence pack. Control board. Maintenance plan.
What the auditor sees.
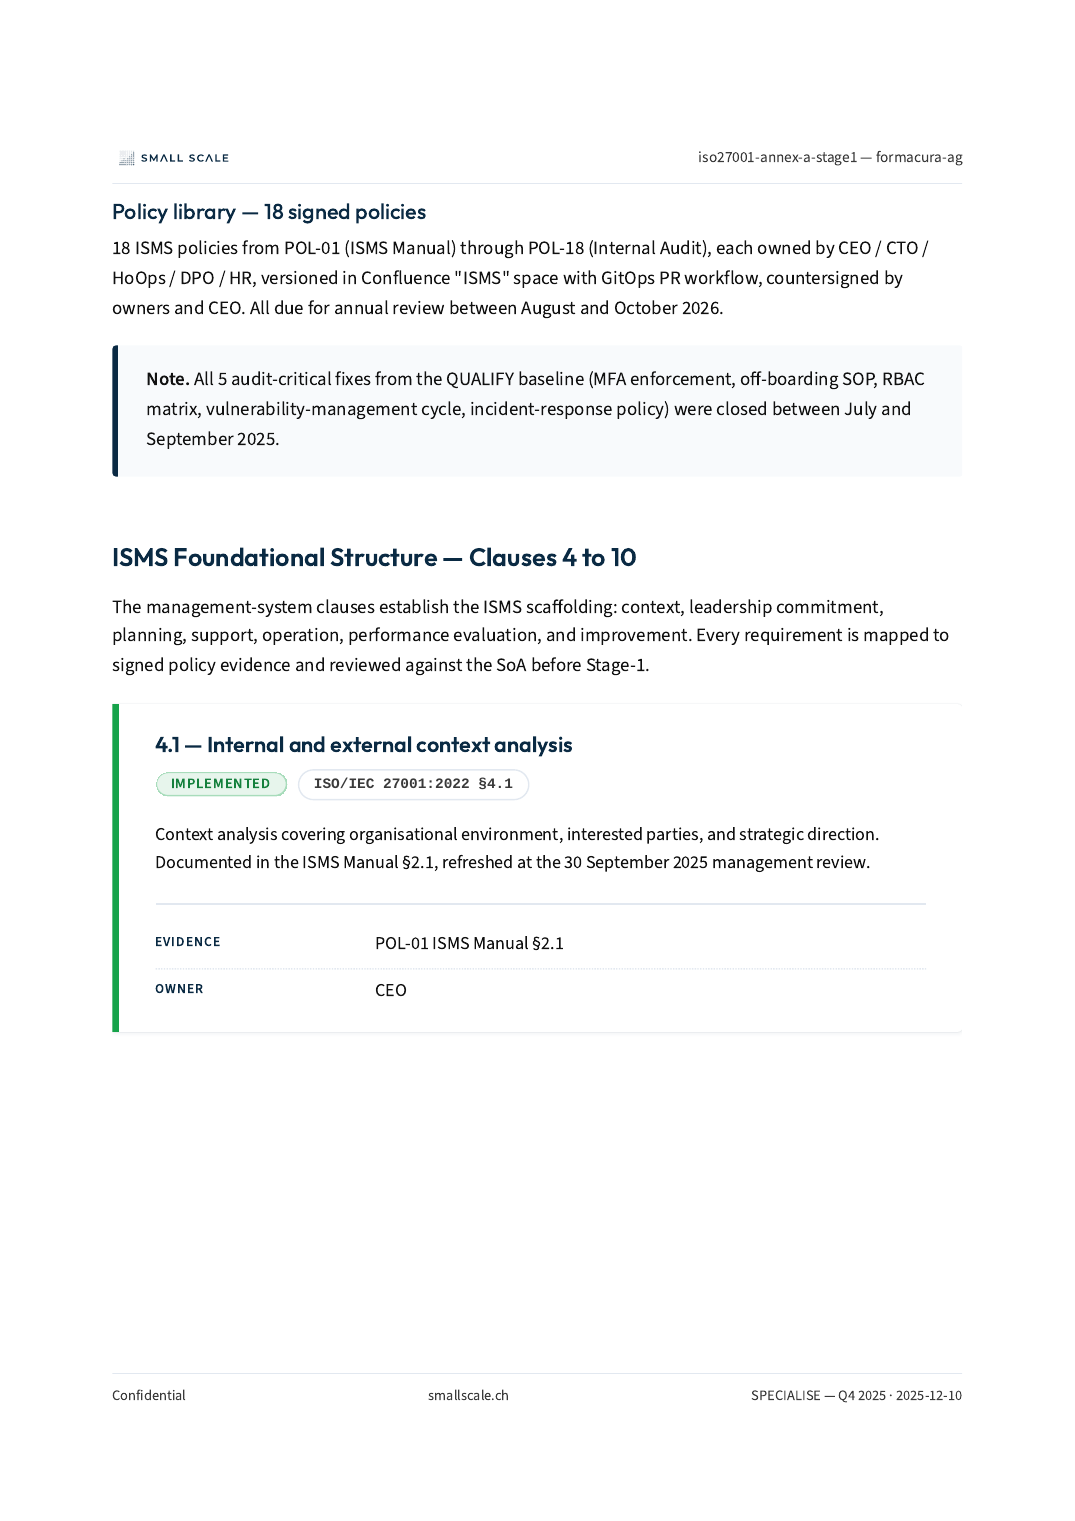
Control board
Living readiness board shown to the auditor.
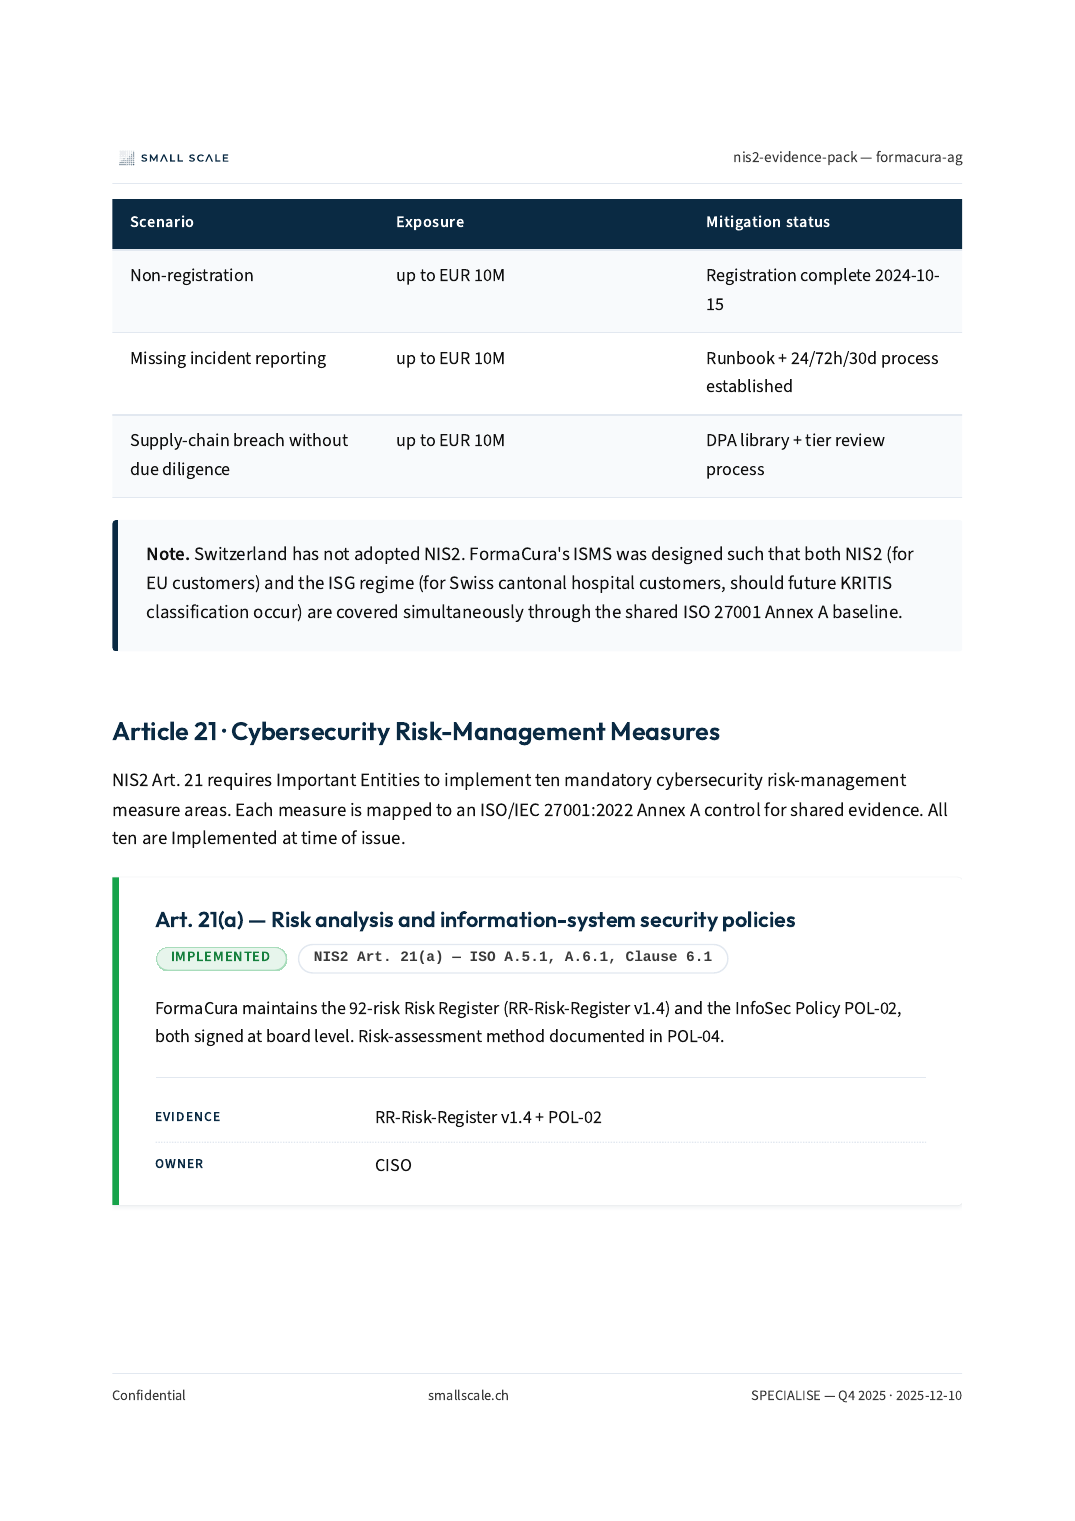
Evidence pack
PDF binder with XLSX exports, audit-ready.
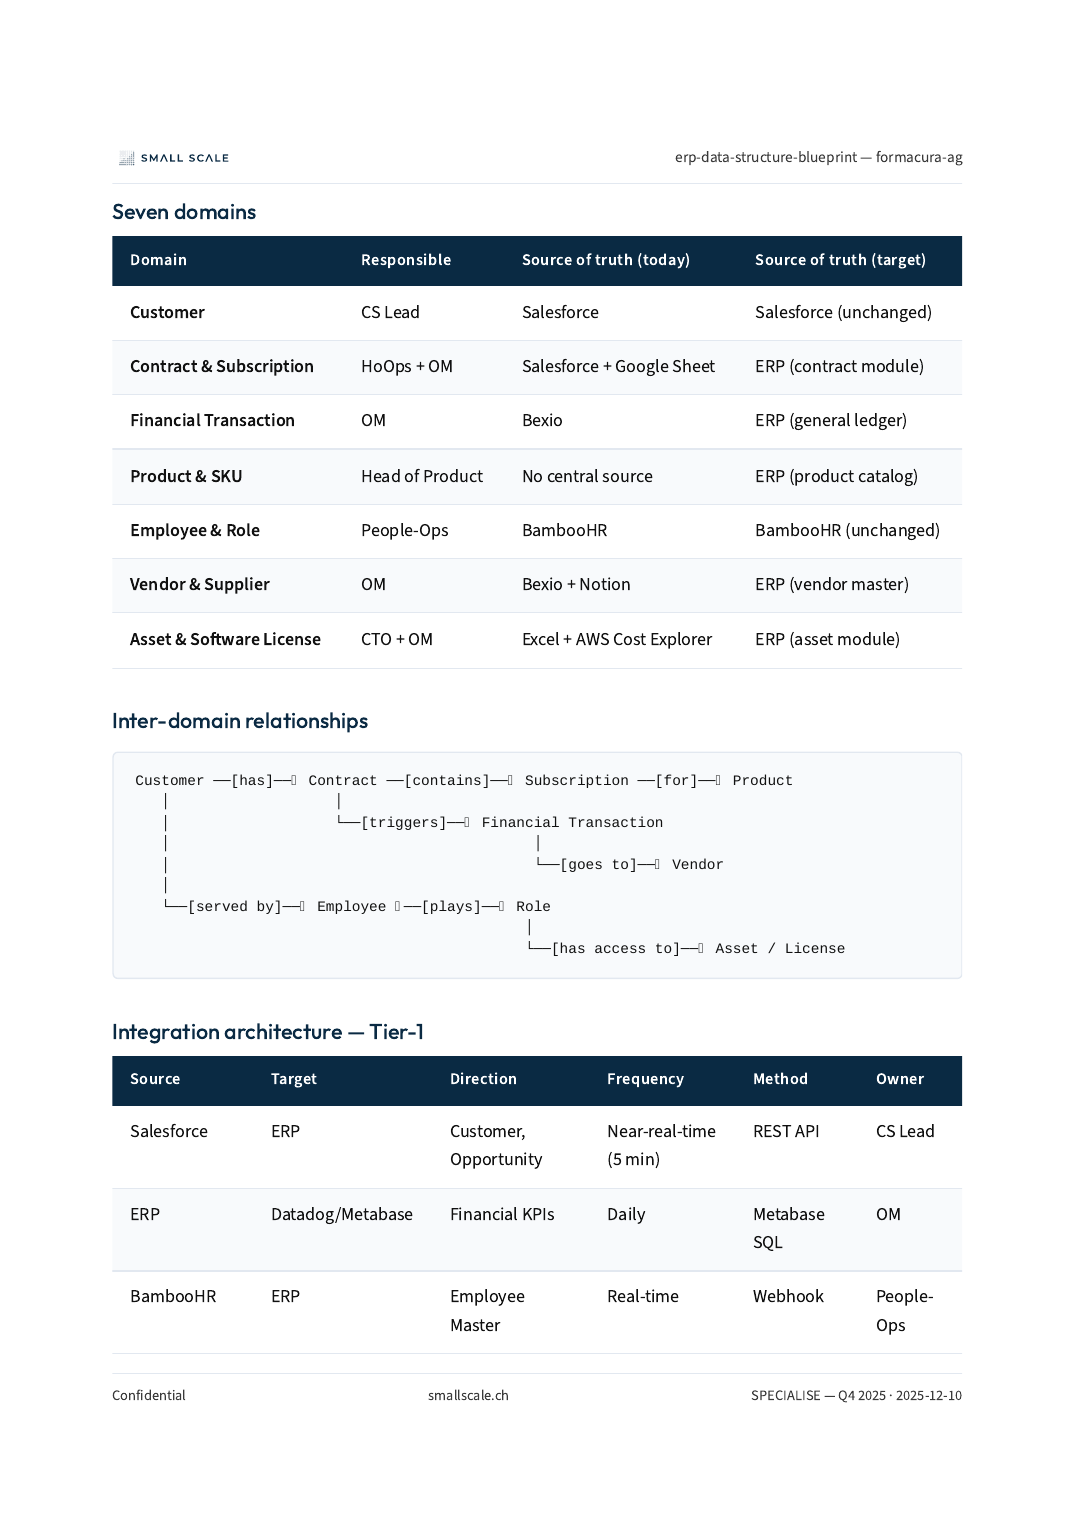
Data-structure blueprint
YAML + ERD, ready for SAP / Dynamics / NetSuite.